ISO 27001 Certification

Simplify your path to global compliance. We offer end-to-end consulting, training, and audit support for ISO, HACCP, CE Mark, and a wide range of international standards.

What is ISO 27001 (Information Security Management System):

ISO 27001 Certification is recognized as an International Standard for information security management. It is defined to help manage organizations in how they can adequately protect sensitive and confidential information for confidentiality, integrity, and access. ISO 27001 essentially helps businesses with the protection from cyber threats of data breaches as well as the unauthorized access in their systems. Compliance with this standard enhances safety and facilitates trust in the client, partners, and stakeholders. It is well applicable to both big and small organizations: IT firms, financial institutions, healthcare providers. Achieving ISO 27001 certification is a testimony of best information security practices ensuring businesses to keep ahead in today’s digital world.

 PopularCert simplifies the ISO 27001 certification process with expert guidance, tailored solutions, and a seamless implementation approach. Our experienced consultants ensure your organization achieves compliance efficiently while strengthening your overall security framework.

Watch our youtube video playlist for complete clause-by-clause series on ISO 27001

How to Get ISO 27001 Certification

ISO-50001-Certification

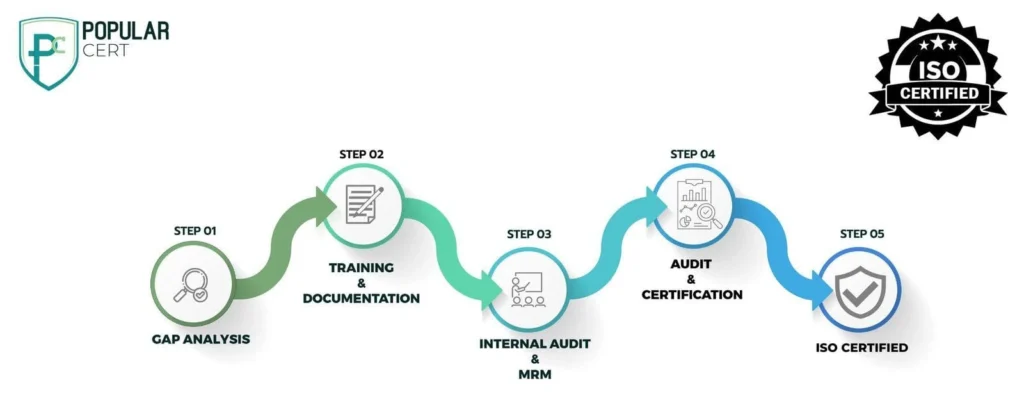
Consultation and Gap Analysis

The starting point of ISMS involves understanding the security practices prevalent in an organization and the requirements. Gap analysis is then done to note existing security controls against ISO 27001 standards and areas that require improvement.

Planning, Documentation, and Policy Development

From the gap analysis findings, a structured implementation plan is developed. It involves setting up security objectives, allocating resources, and defining all the policies, procedures, and documentation needed to comply with ISO 27001 requirements. Such policies are incorporated into the organization's current security framework for improving data protection and risk management.

Training and Awareness

training

Maintaining a competent workforce is essential for continuing effective ISMS. Training sessions are conducted in teaching employees regarding ISO 27001 principles, security best practice, and obligation to safeguard information assets. Awareness programs help ensure that information security becomes part of organizational culture.

Internal Audit and Management Review

Once the ISMS is implemented, it undergoes internal audits to ensure its effectiveness and to identify nonconformities and areas for improvement. Subsequently, the management reviews the same to ensure that the ISMS align with objectives of business, security goals, and regulatory requirements in this regard.

External Certification Audit and Continuous Improvement

shield

An accredited certification body conducts an external audit to verify compliance with ISO 27001 standards. Upon successful completion, the organization receives ISO 27001 certification. To maintain compliance, periodic surveillance audits are conducted, and continuous improvement measures are implemented to enhance security resilience and adapt to evolving threats.

Why Organization Needs ISO 27001

ISO 27001 provides a structured framework to identify, manage, and mitigate information security risks, ensuring business continuity.

  • Cyber threats are becoming increasingly sophisticated.
  • Customers and partners now expect proof of robust security measures.
  • Data protection regulations are stricter than ever.
  • Strong information security practices directly impact financial stability.
  • A security breach can severely damage your organization’s reputation.

Discover practical guidance on building, operating, and improving an ISMS by reviewing our ISO 27001 Certification resources.

Principles of ISO 27001 Information Security Management System (ISMS)

Get Free Consultation

Our Clients

Clients-Logo-Images

Our Projects

Projects-Completed-Images

Why Choose PopularCert?

Types Of ISO Certification
Benefits of ISO 27001 Certification
  1. Stronger Business Reputation: ISO 27001 certification reassures clients and partners that their sensitive data is in safe hands.
  2. A Competitive Edge: Many industries, especially government and large enterprises, now prefer or even require ISO 27001-certified vendors.
  3. Proactive Risk Management: Identify and fix security vulnerabilities before they turn into costly problems.
  4. Smoother Operations: Clear security policies and streamlined processes improve efficiency across your organization.
  5. Regulatory Peace of Mind: Stay ahead of evolving data protection laws and avoid compliance headaches.
  6. Cost Savings: Prevent expensive data breaches, minimize downtime, and reduce response costs with a strong security framework.

Request for expert advice

Cost of ISO 27001 Certification

The cost of ISO 27001 certification depends on many factors, such as size and organizational complexity, number of locations, and the individual certification body. Charges usually include consultancy fees, cost of audits, employee training, and system documentation. Along with these, an annual maintenance cost is required to maintain the certification. It’s a costly investment, but achievement of ISO 27001 certification proves your organization’s commitment to robust information security and adheres to international standards.

Free ISO 27001 Checklist

Assess compliance, reduce risks, and strengthen your information security management.

Why Choose PopularCert for ISO 27001 Certification?

PopularCert makes the process of ISO 27001 certification smooth and hassle-free. They ensure a smooth journey from documentation to audits with expert consultants guiding you at every stage. Their services are customized to meet your business requirements, cost-effective, and without compromising on quality. Whether you are just a startup or an established company, PopularCert will help achieve ISO 27001 certification under the globally accepted standard while helping you maintain your long-term security and compliance. 

FAQ

ISO 27001 is an international standard for information security management systems (ISMS) that helps organizations improve efficiency and customer satisfaction.

Any organization, regardless of size or industry, can get ISO 27001 certified to enhance information security control and gain a competitive edge.

The timeline varies depending on the organization’s size and readiness but typically takes 3 weeks to a Month.

It improves process efficiency, customer satisfaction, compliance, and market credibility, leading to better business growth.

Ready to Get Certified for Your Next Project?

Reach Us Now

Claim Your Free Consultation Today!

New-logo-tiny

Start Your Certification Journey Today

Get Free Consultation and a Clear Roadmap Tailored to your Business