
ISO 27001 Certification in NEOM
Simplify your path to global compliance. We offer end-to-end consulting, training, and audit support for ISO, HACCP, CE Mark, and a wide range of international standards.
- 11+ Years Experience
- 30+ Countries Served
NEOM is one of the world’s most ambitious smart city projects, powered by artificial intelligence, digital infrastructure, renewable energy, and advanced technologies. In such a highly connected and data-driven environment, protecting sensitive information is not optional, it is essential.
ISO 27001 certification in NEOM helps organizations establish a structured Information Security Management System (ISMS) to identify, assess, and mitigate cybersecurity risks. Whether you are a technology startup, construction contractor, financial services provider, or digital infrastructure company operating in NEOM, ISO 27001 demonstrates your commitment to safeguarding data, maintaining regulatory compliance, and building stakeholder trust.
Why Information Security Matters in NEOM
- Smart City Infrastructure
NEOM is built around advanced smart city technologies that rely on interconnected digital systems to manage transportation, utilities, public services, and urban operations. These systems continuously exchange large volumes of data, making them attractive targets for cyber threats. ISO 27001 helps organizations establish strong information security controls to protect critical smart city infrastructure, reduce vulnerabilities, and ensure uninterrupted service delivery. By implementing a structured Information Security Management System (ISMS), businesses can enhance resilience against cyberattacks and support the secure operation of connected city environments.
- AI-Driven Services
Artificial Intelligence plays a key role in NEOM’s vision, supporting automation, predictive analytics, intelligent decision-making, and personalized services. AI systems depend on vast amounts of data, algorithms, and machine learning models that require protection from unauthorized access, manipulation, or theft. ISO 27001 helps organizations secure AI-related information assets, manage risks associated with data processing, and maintain the integrity of AI-driven operations. This ensures reliable outcomes, improves stakeholder confidence, and supports responsible innovation in AI-powered environments.
- IoT Ecosystems
The Internet of Things (IoT) forms the backbone of many smart city and industrial applications in NEOM, connecting sensors, devices, machines, and control systems. While IoT improves efficiency and real-time monitoring, it also introduces cybersecurity challenges due to the large number of connected endpoints. ISO 27001 helps organizations identify and address security risks associated with IoT devices by implementing access controls, network security measures, and monitoring mechanisms. This reduces the likelihood of cyber intrusions and ensures secure communication across the entire IoT ecosystem.
- Cloud Computing Environments
Many organizations operating in NEOM rely on cloud-based platforms for data storage, application hosting, collaboration, and digital service delivery. While cloud computing offers flexibility and scalability, it also requires robust security controls to protect sensitive information. ISO 27001 provides a framework for managing cloud security risks, controlling access to data, and ensuring proper incident response procedures. By adopting ISO 27001, businesses can strengthen data protection, minimize the risk of breaches, and maintain customer confidence in cloud-based operations.
- Data Privacy Challenges
Organizations in NEOM collect, process, and store significant amounts of personal, financial, operational, and business-critical information. Protecting this data is essential to maintain trust and comply with privacy regulations and contractual obligations. ISO 27001 helps organizations establish policies and procedures for handling sensitive information securely throughout its lifecycle. Through risk assessments, access management, and data protection controls, businesses can reduce the risk of data leaks, unauthorized disclosures, and privacy violations while demonstrating a strong commitment to information security.
- Critical Infrastructure Protection
Critical infrastructure such as energy networks, water systems, transportation services, telecommunications, and digital communication platforms are essential to NEOM’s development and daily operations. Any disruption to these systems can have significant economic, operational, and social consequences. ISO 27001 supports organizations in identifying critical assets, assessing potential threats, and implementing effective security measures to safeguard infrastructure from cyberattacks and operational risks. This proactive approach enhances business continuity, improves incident response capabilities, and helps ensure the reliability of essential services across NEOM.
Our ISO 27001 Certification Process Explained Step-by-Step
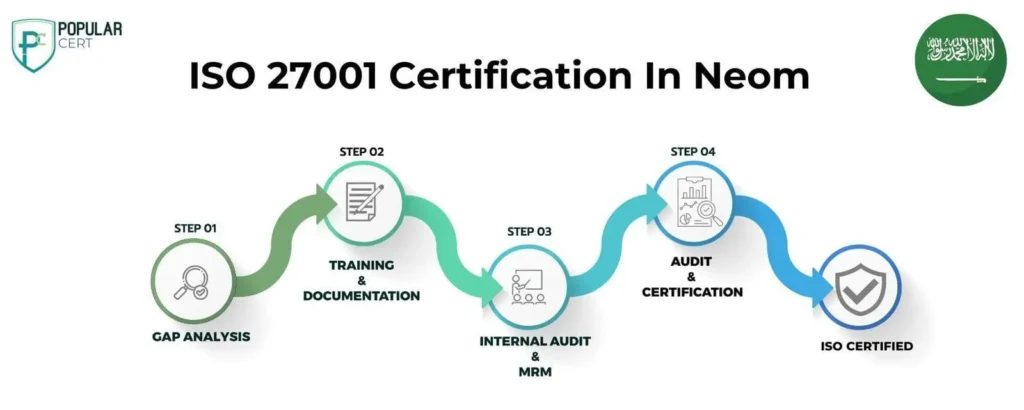
Consultation and Gap Analysis

PopularCert’s experts assess your organization’s unique requirements and current systems in Neom. We conduct a detailed gap analysis to identify areas requiring improvement to align with ISO standards.
Planning, Documentation, and Policy Development

Based on the gap analysis findings, we develop a tailored implementation plan, define resource requirements, and support the creation of essential policies and documentation, ensuring seamless integration into your existing organizational structure.
Training and Awareness

We provide comprehensive training to ensure your team fully understands ISO requirements and their roles in effectively maintaining the management system.
Internal Audit and Management Review

Our specialists conduct internal audits to assess system performance and address any non-conformities. A management review ensures the system aligns with your organization’s objectives and ISO standards.
External Certification Audit and Certification

Upon successfully completing the external audit conducted by the certification body, your organization in Neom will be awarded the ISO 27001 certificate. This certification highlights your commitment to information security management and continuous improvement, showcasing your dedication to safeguarding sensitive data, meeting international security standards, and enhancing credibility and customer trust.
Get Free Consultation
Our Clients

Our Projects
Why Choose PopularCert?
- Trusted Global ISO Certification Partner
- Experienced Industry-Focused Consultants
- Complete End-to-End Certification Support
- Fast & Transparent Certification Process
- International Compliance & Audit Readiness
- Dedicated Long-Term Customer Support
Types Of ISO Certification In Neom
- ISO Certification In Neom
- ISO 9001 Certification in Neom
- ISO 14001 Certification in Neom
- ISO 45001 Certification in Neom
- ISO 22000 Certification in Neom
- ISO 27001 Certification in Neom
- ISO 17025 Certification in Neom
- ISO 13485 Certification in Neom
- CE Mark Certification in Neom
- ISO 20000-1 Certification in Neom
- GMP Certification in Neom
- Halal Certification in Neom
- SOC-1 Certification in Neom
- SOC-2 Certification in Neom
Benefits of ISO 27001 Certification in Neom
- Solid Data Protection: Safeguards sensitive information from unauthorized access and breaches.
- Adherence to Regulations: Ensures compliance with legal and regulatory requirements.
- Enhanced Reputation: Builds trust with clients and stakeholders.
- Competitive Advantage: Differentiates your organization in the market.
- Cost Savings: Reduces the risk of data breaches, leading to lower costs.
- Improved Operational Efficiency: Streamlines processes and enhances productivity.
- Continuous Enhancement: Promotes ongoing improvement in security practices.
What are the ISO 27001 Requirements?
Context of the Organization:
The first step in ISO 27001 is understanding the environment in which your organization operates. This involves identifying internal factors, such as company processes, technologies, and business objectives, as well as external factors like legal requirements, market conditions, and cybersecurity threats. Organizations must also identify interested parties, including customers, employees, suppliers, and regulators, along with their information security expectations. Based on this understanding, the organization defines the scope of its Information Security Management System (ISMS), determining which departments, locations, systems, and information assets will be covered.
Leadership:
Strong leadership is essential for the successful implementation of ISO 27001. Top management must actively support information security initiatives and demonstrate their commitment to protecting organizational data. This includes establishing an information security policy, setting clear objectives, allocating necessary resources, and assigning roles and responsibilities for information security management. When leadership actively participates in security efforts, it helps create a culture where information security becomes a shared responsibility across the organization.
Risk Assessment:
Risk assessment is one of the core requirements of ISO 27001. Organizations must identify potential threats and vulnerabilities that could affect their information assets, such as cyberattacks, data breaches, system failures, or unauthorized access. Each risk is evaluated based on its likelihood and potential impact on the business. Once risks are identified, organizations develop and implement appropriate treatment plans to reduce, avoid, transfer, or accept the risks. Security objectives are then established to help strengthen the organization’s overall security posture.
Support:
To maintain an effective ISMS, organizations need adequate resources, competent personnel, and ongoing support. ISO 27001 requires businesses to provide employee training and awareness programs so that staff understand their information security responsibilities. Effective communication processes should also be established to ensure security-related information is shared appropriately throughout the organization. In addition, companies must create and maintain documented information, including policies, procedures, records, and other documents necessary to support the operation of the ISMS.
Operations:
The operations phase focuses on implementing and managing the information security controls identified during risk assessment. Organizations must put security measures into practice to protect sensitive information and ensure risks are properly managed. This may include access controls, data encryption, backup procedures, incident response plans, and network security measures. The organization must also regularly execute and monitor its risk treatment plans to ensure security controls remain effective and aligned with business objectives.
Performance Evaluation:
ISO 27001 requires organizations to regularly assess how well their Information Security Management System is performing. This involves monitoring security activities, measuring performance against established objectives, and conducting internal audits to verify compliance with ISO 27001 requirements. Management reviews are also conducted to evaluate the effectiveness of the ISMS, identify areas for improvement, and ensure that information security continues to support organizational goals and changing business needs.
Improvement:
Continuous improvement is a key principle of ISO 27001. Organizations must identify and address any nonconformities, weaknesses, or security incidents that may occur within the ISMS. Corrective actions should be taken to prevent similar issues from happening again. By regularly reviewing security performance, updating controls, and adapting to new risks and technologies, organizations can continuously strengthen their information security practices and maintain the effectiveness of their ISMS over time.
What are the Cybersecurity Risks Faced by Businesses in NEOM?
As NEOM is built around smart technologies, IoT devices, AI systems, and cloud-based services, businesses operating in the region face several cybersecurity risks that can affect their operations, finances, and reputation.
1. Cyberattacks:
Cybercriminals may target business networks, applications, and databases to steal sensitive information, disrupt services, or gain unauthorized access. These attacks can result in operational downtime and financial losses.
2. Data Breaches:
A data breach occurs when unauthorized individuals access confidential information such as customer records, employee data, financial information, or intellectual property. Data breaches can damage a company’s reputation and lead to legal or regulatory penalties.
3. Ransomware Attacks:
Ransomware is a type of malware that encrypts business data and demands payment for its recovery. Such attacks can halt business operations, cause significant financial losses, and disrupt critical services.
4. IoT Vulnerabilities:
Businesses in NEOM rely heavily on IoT devices such as sensors, smart meters, cameras, and automated systems. If these devices are not properly secured, attackers can exploit them to gain access to larger networks or disrupt operations.
5. Cloud Security Risks:
Many organizations use cloud platforms to store and process data. Weak security settings, poor access management, or cloud misconfigurations can expose sensitive information to unauthorized users and increase the risk of data loss.
6. Insider Threats:
Employees, contractors, or business partners may intentionally or unintentionally compromise security. Examples include sharing confidential information, using weak passwords, or mishandling sensitive data, which can lead to security incidents.
7. AI System: Manipulation
As AI-powered solutions become more common in NEOM, attackers may attempt to manipulate AI models or alter the data used by these systems. This can lead to inaccurate predictions, poor decision-making, and operational disruptions.
8. Phishing and Social Engineering:
Cybercriminals often use fake emails, messages, or phone calls to trick employees into revealing passwords, financial information, or other sensitive data. These attacks remain one of the most common causes of security breaches.
9. Supply Chain Attacks:
Businesses often depend on third-party vendors, contractors, and service providers. If one of these partners has weak cybersecurity controls, attackers can use that vulnerability to gain access to the business’s systems and data.
10. Critical Infrastructure Disruptions:
Businesses in NEOM depend on reliable power, telecommunications, transportation, and digital infrastructure. Cyberattacks targeting these critical services can cause operational interruptions, financial losses, and reduced productivity.
Industries in NEOM That Benefit from ISO 27001 Certification
ISO 27001 certification is particularly valuable for organizations operating in NEOM’s high-tech and innovation-driven ecosystem, including:
- Smart city technology providers
- Artificial Intelligence and robotics companies
- Renewable energy and infrastructure developers
- Construction and engineering firms
- Financial services and fintech companies
- IT service providers and cloud solution companies
- Healthcare and biotech organizations
With large volumes of sensitive data being processed daily, these industries must implement robust information security frameworks to protect assets and maintain operational continuity.
Case Study:
A company that develops smart infrastructure and IoT sensors received a subcontract worth more than SAR 100 million in the NEOM region. To qualify for the project, NEOM required the company to have an integrated management system and meet strict cybersecurity requirements.
Challenges:
- The company did not have a formal system for classifying data.
- Access control policies were not clearly defined.
- It needed to demonstrate that its AI-powered environmental sensors and HVAC systems complied with international privacy and data protection standards.
Solution:
- Implemented an Information Security Management System (ISMS) to protect sensor data and construction plans.
- Introduced Role-Based Access Control (RBAC) so employees could only access information relevant to their roles.
- Applied data encryption to protect information during storage and transmission.
- Established 24/7 security monitoring and conducted regular penetration testing to meet smart city cybersecurity requirements.
Results:
- Achieved ISO 27001 certification within 9 months.
- Successfully passed NEOM’s vendor registration and cybersecurity assessment process.
- Reduced unauthorized access attempts through continuous monitoring and compliance controls.
- Used the certification to secure additional contracts in other Saudi giga-projects.
- Shortened tender approval and evaluation times, helping the company win new business more quickly.
Cost of ISO 27001 Certification In Neom
The cost of ISO 27001 certification in Neom varies based on factors such as the size of your organization, the complexity of operations, and the current security measures in place. Costs typically include consultancy fees, documentation, employee training, internal audits, and external certification audits. Popularcert offers cost-effective ISO 27001 certification services tailored to your business needs, ensuring compliance with international standards while maintaining budget efficiency. Contact us today to receive a customized quote and expert guidance throughout the certification process.
ISO 27001 Certification in NEOM: Popularcert has trusted ISO consultants in NEOM for Information Security Management Systems at an affordable cost. Contact us today to learn how to get and apply for ISO 27001 certification with expert guidance and cost-effective solutions.
Why Choose PopularCert for ISO 27001 Certification in Neom?
Popularcert is your trusted partner for ISO 27001 certification in Neom, offering expert guidance to help your organization achieve international information security standards. Our experienced consultants provide end-to-end support, including gap analysis, policy development, staff training, and internal audits to ensure a smooth certification process. We prioritize cost-effective solutions tailored to your business needs while maintaining compliance with ISO 27001 requirements. With Popularcert, you can safeguard sensitive data, boost customer trust, and demonstrate a strong commitment to information security. Contact us today for reliable and efficient ISO 27001 certification services.
Secure Your Data. Win Client Trust. Get ISO 27001 Certified in NEOM Today.
Talk to our experts now and receive a clear roadmap, timeline, and cost estimate tailored to your business. Take the first step toward stronger security and faster business growth.
FAQ
What is ISO 27001 certification?
ISO 27001 is an international standard for Information Security Management Systems (ISMS). It provides a framework to protect sensitive data, manage risks, and ensure continuous improvement in information security practices.
Why is ISO 27001 important for businesses in Neom?
ISO 27001 helps businesses protect critical information, comply with global security standards, build customer trust, and reduce data breach risks. It also enhances credibility when dealing with international clients and partners.
How can I apply for ISO 27001 certification in Neom?
To apply, contact Popularcert for expert consultancy services. We will guide you through the process, including gap analysis, policy development, internal audits, and certification audits.
What industries can benefit from ISO 27001 in Neom?
ISO 27001 is beneficial for all industries handling sensitive data, including IT, finance, healthcare, government, and manufacturing sectors.
How much does ISO 27001 certification cost in Neom?
The cost varies based on company size, complexity, and existing systems. Popularcert offers tailored packages for competitive pricing.
- Join 1000+ Certified Companies
Ready to Get Certified for Your Next Project?
- Free Consultation
- Expert Guidance
- Fast Turnaround
Reach Us Now
Claim Your Free Consultation Today!