
ISO 27001 Certification In Quezon
Simplify your path to global compliance. We offer end-to-end consulting, training, and audit support for ISO, HACCP, CE Mark, and a wide range of international standards.
- 11+ Years Experience
- 30+ Countries Served
ISO/IEC 27001 certification in Quezon City demonstrate that their information security management system (ISMS) has been independently assessed against an internationally recognized standard. It provides a systematic approach to identifying information security risks, selecting appropriate controls, and continually improving how sensitive information is protected.
Businesses that manage customer records, financial information, employee data, software systems, or confidential business documents can use ISO 27001 to establish clearer security responsibilities and more consistent risk-management practices. The standard can be relevant to IT service providers, business process outsourcing (BPO) companies, professional service firms, healthcare organizations, and other businesses that depend on reliable information handling.
PopularCert supports organizations with gap assessments, risk assessment guidance, ISMS documentation, implementation planning, staff awareness, and audit preparation. An independent certification body conducts the certification audit and makes the certification decision.
How to Get ISO 27001 Certification In Quezon ?
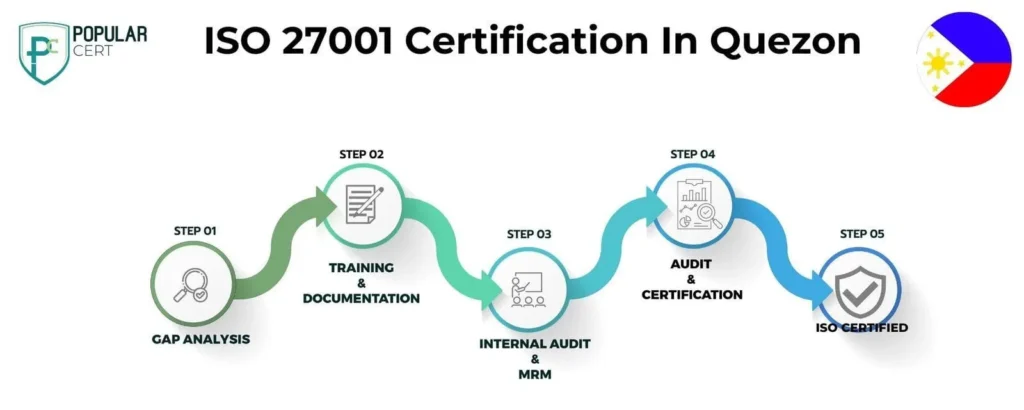
Consultation and Gap Analysis

PopularCert’s experts evaluate your organization’s existing information security management system (ISMS) and specific requirements. We conduct a detailed gap analysis to identify areas that need improvement to comply with ISO 27001 standards.
Planning, Documentation, and Policy Development

Based on the gap analysis, we develop a tailored implementation plan, outline resource requirements, and assist in creating essential policies and documentation. These are seamlessly integrated into your organization’s security framework.
Training and Awareness

We provide comprehensive training to ensure your team understands ISO 27001 requirements, security controls, and their role in maintaining a robust ISMS.
Internal Audit and Management Review

Our team conducts internal audits to assess the effectiveness of your ISMS and address any non-conformities. A management review ensures alignment with organizational objectives and ISO 27001 standards.
External Certification Audit and Certification

Once the external audit by the certification body is successfully completed, your organization will receive the ISO 27001 certification. This certification highlights your commitment to information security, enhances data protection, strengthens risk management, and builds trust with clients and stakeholders.
ISO 27001 Documentation and Evidence to Prepare
ISO 27001 requires documented information appropriate to the standard’s requirements and the organization’s ISMS. The exact documentation and operational evidence depend on the scope, risk assessment, selected controls, and how the system is implemented.
Preparation may include:
- The defined ISMS scope and information security policy.
- The organization’s approach to assessing and treating information security risks.
- Risk assessment results and the risk-treatment plan.
- The Statement of Applicability, including the status and justification of relevant controls.
- Information security objectives and plans for achieving them.
- Records of relevant training, monitoring, internal audits, management reviews, and corrective actions.
- Evidence that applicable security controls are implemented and operating.
The goal is not to produce paperwork for its own sake. Documentation and records should accurately reflect the organization’s security arrangements and provide evidence that the ISMS is maintained and improved.
Information Security Risks ISO 27001 Can Help Quezon City Businesses Manage
Organizations can face information security risks when employees access sensitive files, external providers process business data, systems are changed without adequate review, or access rights remain active after job responsibilities change. These risks can affect confidentiality, service continuity, customer relationships, and business operations.
ISO/IEC 27001 requires organizations to establish an ISMS appropriate to their context, assess information security risks, and determine how those risks will be treated. The specific controls depend on the organization’s risks, scope, and applicable requirements.
Get Free Consultation
Our Clients

Our Projects
Why Choose PopularCert?
- Trusted Global ISO Certification Partner
- Experienced Industry-Focused Consultants
- Complete End-to-End Certification Support
- Fast & Transparent Certification Process
- International Compliance & Audit Readiness
- Dedicated Long-Term Customer Support
Types Of ISO Certification In Quezon
- ISO Certification In Quezon
- ISO 9001 Certification in Quezon
- ISO 14001 Certification in Quezon
- ISO 45001 Certification in Quezon
- ISO 22000 Certification in Quezon
- ISO 27001 Certification in Quezon
- ISO 17025 Certification in Quezon
- ISO 13485 Certification in Quezon
- CE Mark Certification in Quezon
- ISO 20000-1 Certification in Quezon
- GMP Certification in Quezon
- Halal Certification in Quezon
- SOC-1 Certification in Quezon
- SOC-2 Certification in Quezon
Depending on their operations, businesses in Quezon City may need to examine:
- Access management: Whether employees and third parties have appropriate access to information and systems.
- Supplier security: How external IT providers and other relevant suppliers are assessed and monitored.
- Incident response: How suspected security incidents are reported, investigated, and addressed.
- Information handling: How sensitive data is stored, shared, retained, and disposed of.
- Business continuity: How information and essential services are protected against relevant disruptions.
- Staff awareness: Whether employees understand their information security responsibilities.
The purpose is not to adopt every possible security measure indiscriminately. It is to identify relevant risks, select suitable treatments and controls, and maintain evidence that the ISMS is operating as intended.
ISO 27001 and Data Protection Responsibilities in the Philippines
Organizations that handle personal information in the Philippines may have obligations under applicable privacy and data protection laws. ISO 27001 can support a structured approach to managing information security risks, but certification does not automatically establish compliance with every legal requirement.
Businesses should assess which privacy, contractual, sector-specific, and other obligations apply to their activities. They should also distinguish information security controls from broader responsibilities relating to the collection, use, retention, disclosure, and lawful processing of personal information.
The appropriate approach depends on the organization’s role, the types of information it handles, and the requirements that apply to its operations. Legal or privacy-specific questions should be reviewed against current official Philippine guidance or with a qualified adviser.
Defining the ISO 27001 Certification Scope
The scope of ISO 27001 certification determines which parts of an organization are covered by its information security management system. It should reflect the organization’s activities, locations, information assets, technologies, responsibilities, and relevant interfaces with other parties.
For example, a business may propose a scope covering its managed IT services, software development activities, customer support operations, or a defined business unit. The appropriate scope depends on how the organization operates and which activities it intends to include in the ISMS.
Before finalizing the scope, organizations should consider:
- Which services, teams, and business activities will be included.
- Where relevant information is created, stored, processed, and accessed.
- Which systems, facilities, and external providers support the included activities.
- What interfaces or dependencies exist between the proposed scope and other parts of the organization.
- Whether the scope is clear, practical, and consistent with the actual operation of the ISMS.
A clearly defined scope helps establish what the certification assessment covers. Certification should not be presented as covering business activities, locations, or systems that fall outside the approved scope.
Business Benefits of an Effective ISO 27001 Management System
ISO 27001 can help organizations build a structured approach to information security rather than relying on isolated technical measures. The benefits depend on how effectively the ISMS is implemented, maintained, and reviewed.
- Risk-based security decisions: Helps management prioritize information security risks according to defined criteria and business needs.
- Clearer security responsibilities: Establishes responsibilities for managing information security across relevant teams and activities.
- More consistent controls: Supports the planned implementation and monitoring of controls selected through the organization’s risk-treatment process.
- Improved incident preparedness: Helps formalize relevant procedures for reporting, assessing, and responding to information security incidents.
- Supplier risk oversight: Supports the management of information security risks associated with relevant external providers.
- Stronger customer assurance: Certification can provide independent evidence that the assessed ISMS meets the standard’s requirements.
- Continual improvement: Encourages organizations to review performance, address nonconformities, and improve the management system over time.
ISO 27001 certification does not eliminate all cyber risks or automatically establish compliance with every applicable privacy or cybersecurity law. Organizations remain responsible for meeting their legal, contractual, and operational obligations.
What Determines the Cost of ISO 27001 Certification in Quezon City?
The cost of ISO 27001 certification in Quezon City depends on the scope and complexity of the information security management system, the number of employees and locations involved, the sensitivity of the information handled, the maturity of existing security controls, and the time required for assessment.
Common cost components include:
- Initial gap assessment and implementation consulting.
- Information security risk assessment and treatment planning.
- Development or improvement of ISMS documentation.
- Staff awareness and relevant training.
- Technical or operational improvements identified during implementation.
- Internal audit and corrective-action activities.
- Independent certification audit fees and ongoing surveillance audits.
Consulting costs and certification-body fees are separate. Additional expenditure may be needed where existing controls, systems, or processes require improvement. The most useful estimate comes after reviewing the proposed ISMS scope and the organization’s current level of readiness.
How Long Does ISO 27001 Certification Take in Quezon City?
The time required to prepare for ISO 27001 certification varies by organization. A business with established security processes and a clearly defined scope may require less preparation than one that needs to develop its ISMS, improve existing controls, or coordinate activities across several locations.
Factors that influence the timeline include:
- The size and complexity of the proposed ISMS scope.
- The maturity of existing information security practices.
- The time needed to assess risks and implement treatment actions.
- Staff availability and management involvement.
- The completion of internal audits, management reviews, and corrective actions.
- The availability and scheduling of the independent certification body.
An implementation schedule should be set after an initial assessment. Organizations should avoid choosing a target date before understanding the work needed to establish and demonstrate an effective ISMS.
ISO 27001 Consulting and Certification Readiness Support in Quezon City
PopularCert supports organizations preparing to implement an information security management system in line with ISO/IEC 27001. The work should reflect the organization’s information assets, business activities, risk profile, and proposed certification scope.
Depending on the agreed engagement, support can include:
- Reviewing existing information security practices and identifying gaps.
- Helping define the ISMS scope and implementation priorities.
- Supporting risk assessment and risk-treatment planning.
- Assisting with relevant policies, procedures, and documented information.
- Guiding staff awareness, internal audit preparation, and management review.
- Reviewing readiness for assessment by an independent certification body.
The aim is to help your organization establish a workable management system that addresses relevant risks and can be evaluated against the standard’s requirements. The independent certification body remains responsible for the certification audit and decision.
FAQ
What is ISO 27001?
ISO 27001 is an international standard for Information Security Management Systems (ISMS), ensuring organizations protect sensitive information, manage risks effectively, and maintain data confidentiality, integrity, and availability.
What are the Benefits of ISO 27001 certification?
The Information Security Management System presented in ISO 27001 can help a business to protect sensitive data, meet regulatory compliance, provide business continuity, reduce costs, enhance company culture, adapt to emerging threats and safe-guard themselves from any kind of cyber security breaches or threats.
Who Should Get ISO 27001 Certification in Quezon?
Organizations in Quezon handling sensitive information, such as IT companies, financial institutions, healthcare providers, and government agencies, should get ISO 27001 certification to ensure robust data security and build trust.
How Does ISO 27001 Certification Work in Quezon?
ISO 27001 certification in Quezon involves implementing an Information Security Management System (ISMS), conducting risk assessments, improving data protection processes, and undergoing audits by accredited bodies to ensure compliance with international standards.
- Join 1000+ Certified Companies
Ready to Get Certified for Your Next Project?
- Free Consultation
- Expert Guidance
- Fast Turnaround
Reach Us Now
Claim Your Free Consultation Today!